Enterprise AI control platform
Discover, govern and secure every way your organization uses AI
Vayon AI brings employees, systems, developers and agents under one AI governance layer — discovering how AI is used, understanding what the organization uses it for, enforcing policy before execution, routing each eligible request to an approved destination, governing cost and preserving evidence of what actually happened.
AI entry points
Vayon in 88 Seconds
See fragmented AI become governed AI.
Follow an employee, a developer, a business application and an AI agent as Vayon discovers unmanaged use and brings approved AI activity under one identity, policy, routing and evidence layer.
Read the Transcript
Transcript
AI is already everywhere in your organization. Employees, developers, applications, and agents reach AI through different tools and providers, creating fragmented identities, policies, costs, and evidence.
Vayon uses telemetry from the systems you already operate to discover Shadow AI without deploying another agent to every endpoint.
Vayon brings it all under one governed control layer across employees, developers, applications, and AI agents.
Before eligible execution, Vayon identifies the caller, understands the request, applies policy, selects the right destination, and records safe decision evidence.
Developers keep the tools they prefer, connecting through one governed endpoint instead of every provider directly.
Agents operate with governed identities and explicit permissions. Significant actions pause for approval and leave reviewable evidence.
And the control layer stays in your environment — your identity, your data, your model choices.
Vayon AI, one secure way to use, build, and run AI across your organization.
01
AI adoption outpacing organizational control
Across the organization, AI is reaching people and systems through different tools, models and providers — often faster than security, IT and governance can keep up.
Fragmented AI Usage
Employees, developers and systems reach AI through different tools and providers.
Information Risk
Sensitive organizational information can reach destinations it was never intended to reach.
Uncontrolled Cost
AI spend spreads across models, providers, teams and applications.
Limited Visibility
IT cannot govern what it cannot see.
03
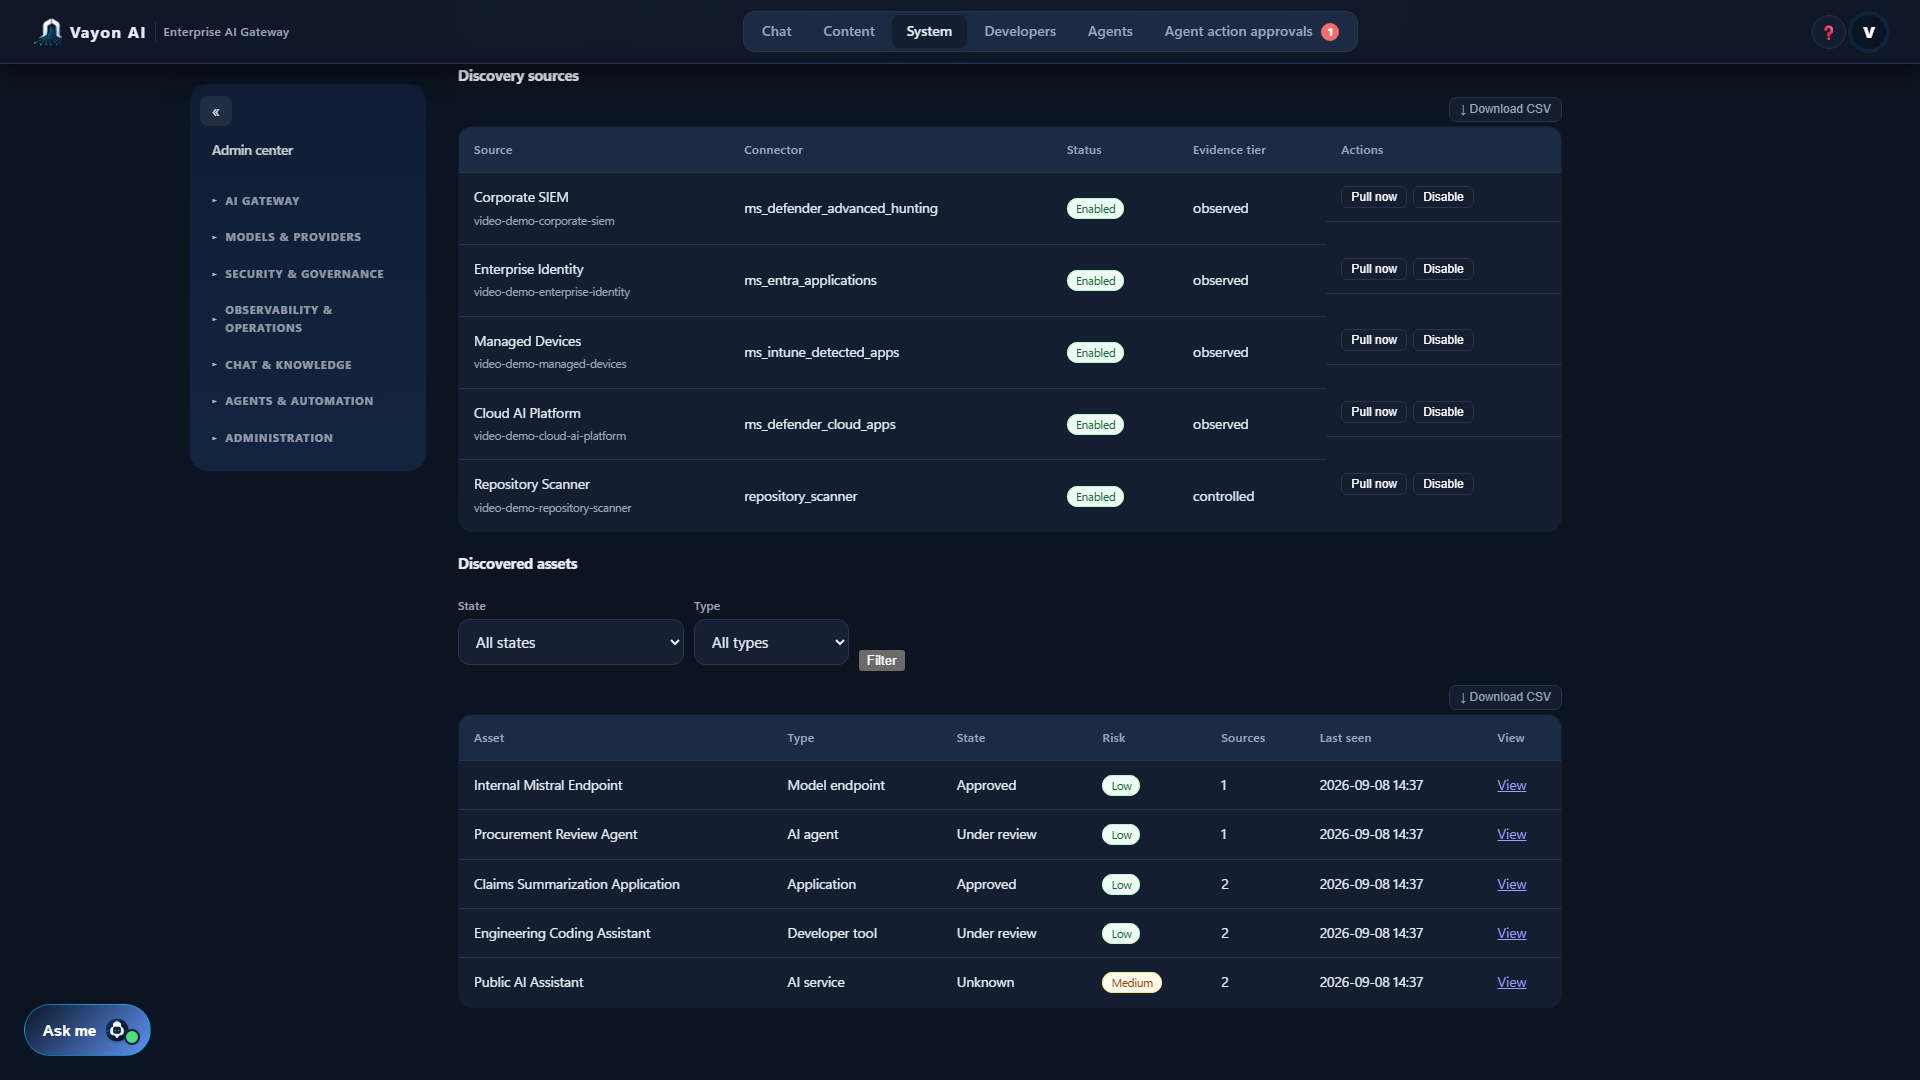
What the organization is actually doing with AI
Vayon AI connects observed AI activity to business use cases. See what the organization declared, what actually happened, where activity occurred, and where observed behavior has drifted from the intended use or risk posture — with governed execution and external observation kept apart rather than merged into one number.
04
One governed layer between your organization and AI
Every governed request is evaluated before an eligible AI destination is selected. Identity, policy, sensitivity and authorization establish what is allowed; capability, availability, reliability and cost help determine the Best Eligible Fit inside that allowed set. Availability never overrides policy. Decision evidence records safe metadata — not raw sensitive prompt content.
AI entry points
- Employee / governed chat
- Developer / IDE
- Business system / API
- Agent / automation
Checked before execution
Vayon AI Gateway
- Identify
- Classify
- Policy
- Eligible candidates
- Best Eligible Fit
Eligible outcome
- Internal Models — Eligible
- Approved Cloud Models — Eligible
- Stopped before execution
After the decision Metering Safe Audit Metadata
Illustrative example — an example routing decision, not live telemetry. Representation built in HTML on synthetic data — not a capture of the running system. See the full flow
05
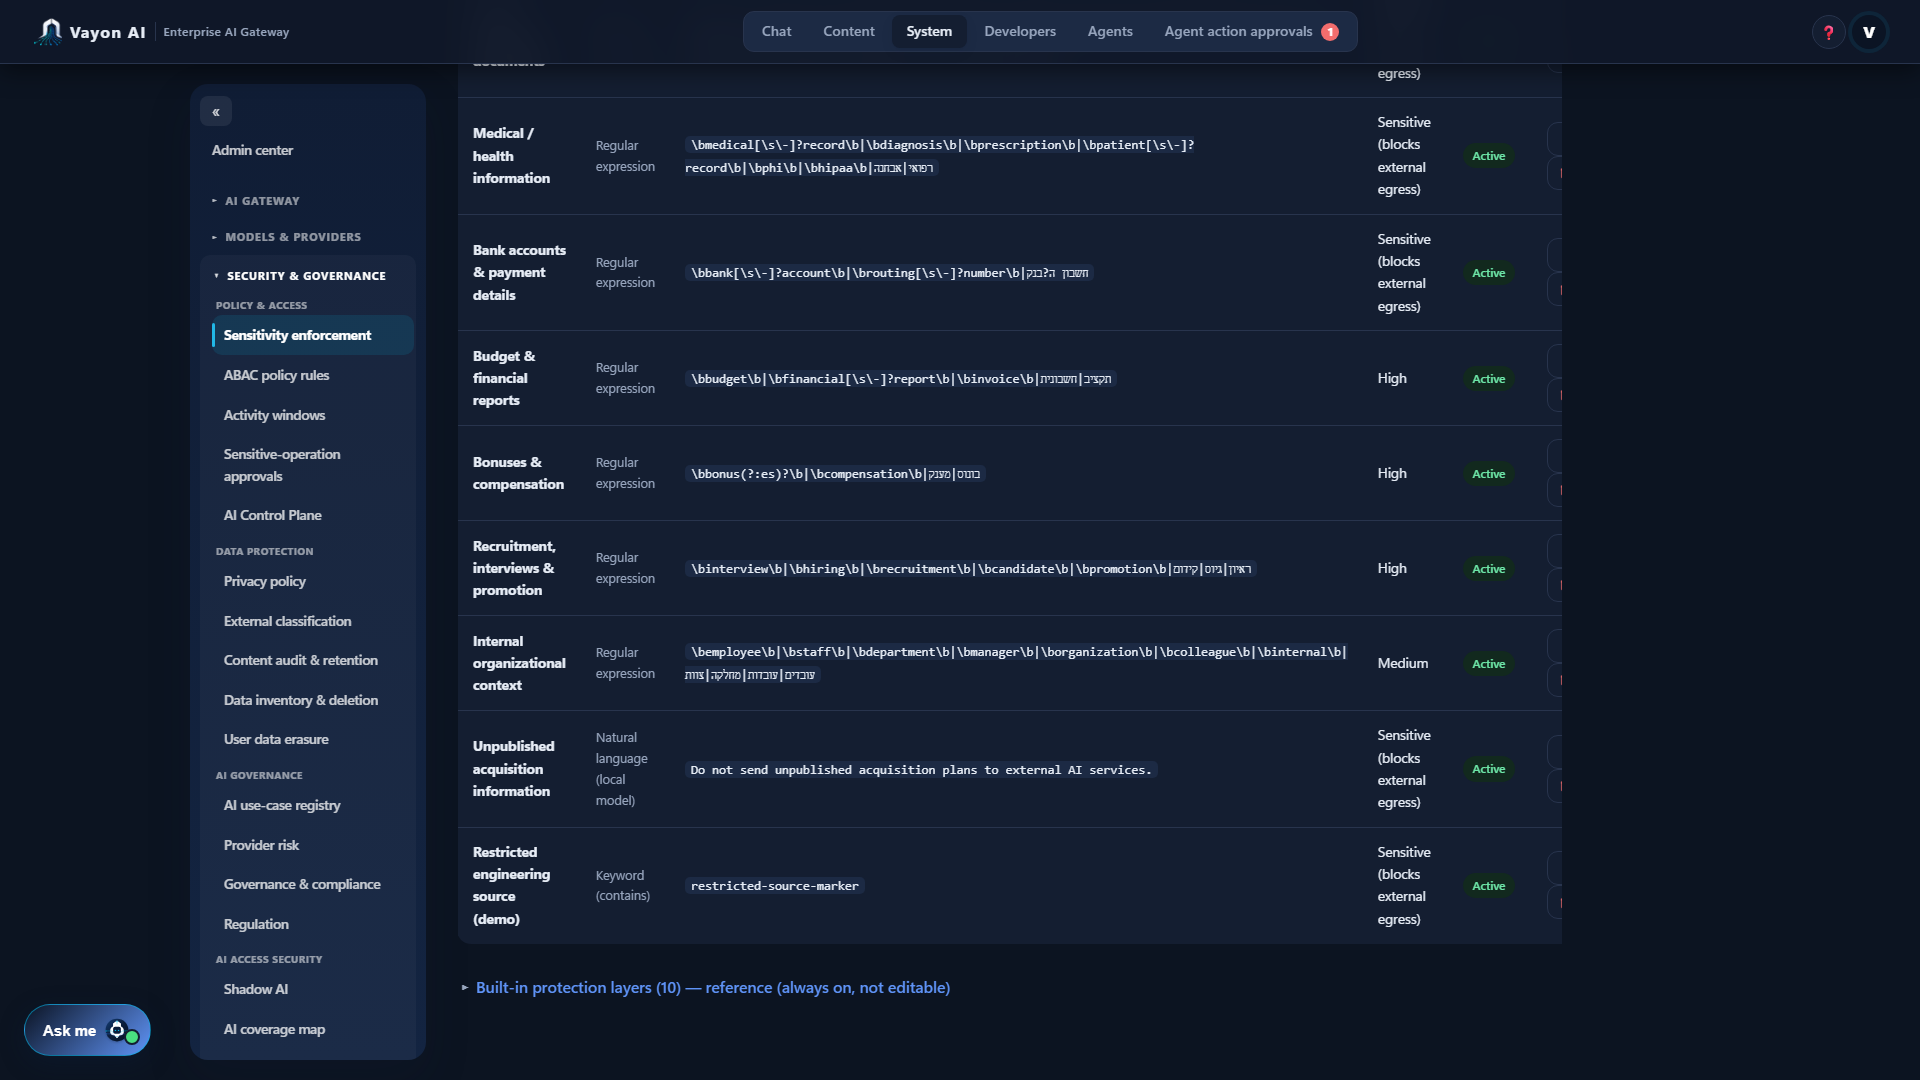
Policy written in natural language, evaluated in context
Security teams can describe organizational policy in natural language. Vayon AI evaluates the user, role, destination, requested action, business context and meaning of the request before execution. Deterministic controls remain available where exact matching is required, but protection is not limited to regex rules or keyword lists.
Example policy
“Don’t allow customer data to leave the organization through an AI tool, unless the destination is an approved, contracted vendor.”
Example decision
“Blocked — destination is not on the approved vendor list for this data classification.”
- Understand
- Evaluate context
- Apply policy
- Allow, block, redact or route
06
Governance where people actually use AI
Vayon AI includes the access experiences and integrations that bring employees, developers, business systems and agents under the same organizational controls.
Vayon AI Workspace
A governed AI workspace for employees - organizational knowledge, document and data-file work, private history, citations and governed model access.
Managed Browser
Apply organizational policy when employees use configured supported public AI services from managed browsers.
Vayon AI for VS Code
Govern coding assistance inside the developer workflow.
Developer AI Tools
Compatible coding clients such as Claude Code and Codex can be pointed through the organizational gateway where the documented setup supports it.
Business Systems & APIs
Applications integrate through a governed API surface instead of embedding provider governance independently.
Agents & Automation
Govern identity, permissions, resources, approvals and evidence for supported agent workflows.
07
AI economics, governed without weakening control
Vayon AI makes AI cost visible, attributable and governable. Price data, usage evidence, budgets, connected-system caps and cost-aware routing help reduce avoidable external spend, while policy, trust and capability always remain ahead of price. Holding every model connection and provider identity in one control plane — instead of one per application — also means changing models without rebuilding governance.
Central Control
One place to see and govern organizational AI activity.
Cost Control
Track estimated spend, usage, attribution, forecasts and efficiency across AI activity.
Business Continuity
Use multiple eligible models and providers while keeping policy authoritative.
Technology Independence
Adopt new models and providers without rebuilding governance each time.
Domain-Scoped Knowledge
Employees get answers from organizational knowledge without duplicated risk — authorization runs before retrieval, so each person sees only what they are permitted to see.
08
Security that extends what you already run
Every request is classified, authorized and checked against policy before anything leaves your control. Vayon AI connects into the security operations you already run rather than asking you to replace them.
Information Protection
Sensitive context is handled according to organizational policy before eligible model execution.
Safe AI Expansion
Extend AI to more teams and use cases under the same controls.
Integrates With Existing Defenses
Governed events reach your SIEM for incident visibility, provider and model containment, and audited emergency controls — Vayon AI connects to your security operations, it does not replace them.
09
Why organizations choose Vayon AI
One platform to see, govern and secure organizational AI use — built to fit into the systems and teams you already have.
Discover
See where AI is already being used across the organization, without deploying a new endpoint agent for that path.
Govern
Apply context-aware policy to AI requests before they reach a destination, not after the fact.
Connect
Work with the security, identity and AI systems you already run, instead of replacing them.
Choose
Route requests to the best eligible internal or approved cloud model for the task.
Operate
Run within infrastructure you control, with no dependency on Vayon at request time.
Retain control
Keep decision evidence and audit metadata inside your own environment, always.
10
VAYON Core and four organization-wide extensions
VAYON Core is the Enterprise AI Gateway and AI control plane — one governed surface for organizational AI. Four optional extensions add capabilities around it, each licensed once per organization and available on every licensed VAYON server.
VAYON Core
The Enterprise AI Gateway and AI control plane — licensed per organization, first licensed VAYON server included.
- AI Gateway & system integrations
- Hybrid routing across internal and approved cloud models
- Security & policy before execution
- Data & egress protection
- Observability, audit & decision evidence
- Governance & compliance evidence
- Models & providers under one control plane
- FinOps & operations
Extend Vayon AI around your AI workloads
Chat & Knowledge
Governed employee chat over organizational knowledge, with citations and content controls.
Agent Platform
Build and govern AI agents — Agent Studio, explicit resource grants, human approval and run evidence.
Developer AI Governance
Developer Portal and IDE integration that govern AI coding assistants. System integrations stay in Core.
Endpoint AI Governance
Discover and govern Shadow AI and browser AI use at the endpoint.
Extensions are licensed once per organization and apply across all licensed VAYON servers — never per server, never per user.
11
Your control layer stays under your control
Vayon AI is designed to run under your control, in your environment, on your terms.
- Customer-controlled deployment.
- Internal and private models as first-class destinations.
- Offline signed licensing.
- No online activation.
- No vendor phone-home dependency.
- No self-update dependency.
- External AI only where configuration and policy permit it.
Authorized integrators can deliver local installation, implementation, training and operational services.